#infosec

3492 posts · Last used 12h

Want to know something funny? I routinely monitor GitHub for keywords, keys and domains related to the infrastructure and products I am responsible for protecting. This week I got an alert because one of those domains showed up in someone’s public repository. I looked into it. This was from what appears to be someone trying to start a competitive company - but the issue was that they’d created their entire stack in public repos, and our domain came up because they’d also committed the Claude prompts they’d used to generate said code - and those prompts included the instructions to copy the material on our domain - which is where the alert came from. Obviously this stuff happens all the time and has done for years, it’s just that now, it’s easier than ever to discover it at light speed because people are using tools they don’t understand to do it. Anyway I opened a PR suggesting they do their own work and also lock down their repo. #infosec
54
0
28
0
#infosec #introduction #FediHire I lead a small data science team at a regional hospital network in the US Midwest. Asking from a place of total ignorance and respect for the infosec community on the Fedi. I'm looking for guidance on securing our laboratory infrastructure. Other teams at our institution shoulder this responsibility, but threats seem to be accelerating among lay users, and I want my team to be proactive. (1/)
0
0
1
0

Has anybody here solved the following conundrum?

  • wanting a bluetooth/gps tracker to be able to recover a stolen bicycle (or other use case)
  • not trusting Google, Apple and other companies to not use/sell/lose data
  • using a deGoogled phone and Linux computer (in my case, LineageOS and Fedora)

That is, I would want to be able to recover my bicycle if stolen, while keeping my daily movements as private as possible. Enshittified web search has not helped much..

#askFedi #fediHelp #bikeTooter #bicycle #cycling #biking #security #privacy #infoSec #opSec #deGoogle #lineageOS #linux #fedora

1
5
3
0
Hi Infosec.Exchange. I'm Ilja Krasnjanski, an independent security researcher. This year I reconstructed UNK_DeadDrop, a fake-job-interview campaign aimed at developers, from retained artifacts without running a sample: a 14-part series, a paper, and an open-source static scanner with YARA rules. I'll post the findings here one at a time. https://krasforge.github.io/UNK_DeadDrop/ #introduction #infosec #ThreatIntel #malware
5
0
5
0
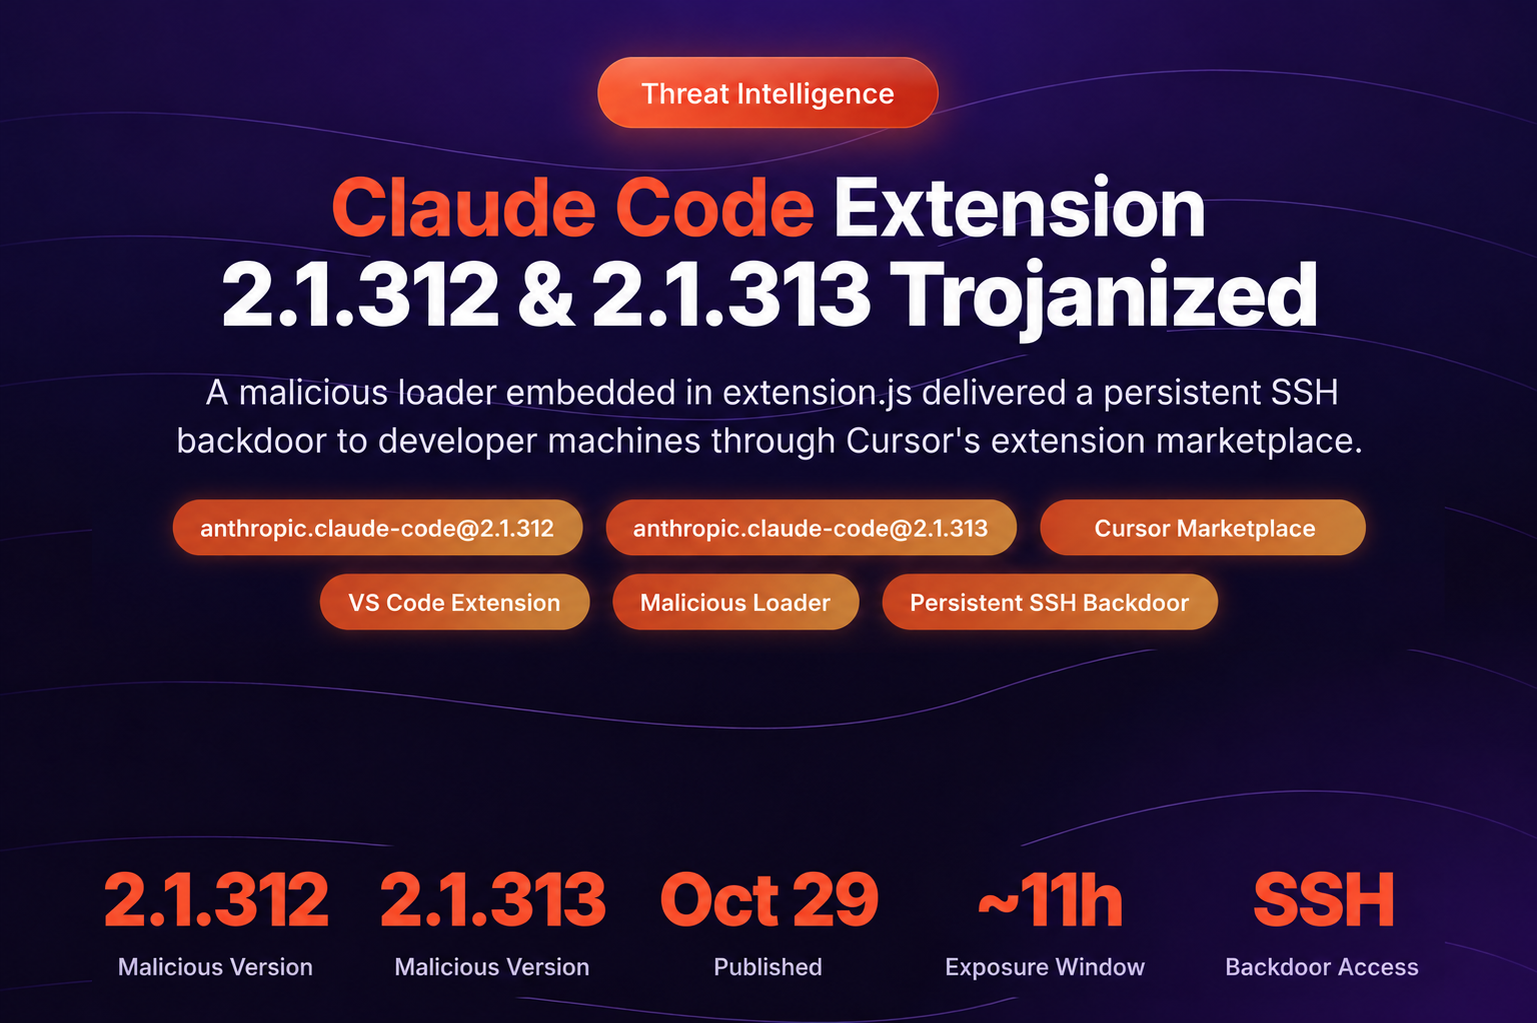
This is the best coverage I've found so far of the Claude Code for VS Code backdoor: https://www.stepsecurity.io/blog/claude-code-extension-trojanized T̵h̵e̵ ̵c̵o̵m̵p̵r̵o̵m̵i̵s̵e̵d̵ ̵v̵e̵r̵s̵i̵o̵n̵ ̵m̵a̵d̵e̵ ̵i̵t̵ ̵i̵n̵t̵o̵ ̵a̵l̵l̵ ̵o̵f̵ ̵t̵h̵e̵ ̵e̵x̵t̵e̵n̵s̵i̵o̵n̵ ̵r̵e̵g̵i̵s̵t̵r̵i̵e̵s̵.̵ EDIT: WRONG! It was just the Cursor Marketplace. Step Security has updated their article to remove statements to the contrary. It's unfortunate that they went off half-cocked and spread misleading information for a day. #infosec #ClaudeCode #ThreatIntelligence
13
0
17
0
Hi everyone! 👋 I'm Kushal, a cybersecurity student working toward a SOC analyst role. I built Intel60 (https://intel60.app) every 30 min it turns news from 8 security outlets + CISA KEV into 60-word, severity-rated briefs with CVSS, EPSS and "actively exploited" tags. Free, no sign-up, no ads. Here to learn from the blue team community. Feedback very welcome! #introduction #infosec #cybersecurity #blueteam #threatintel #SOC
0
0
1
0

** Help me find profiles to follow ... ***

Looking for these kinds of accounts to follow to keep informed on software and papers: ActivityPub and Fediverse hosters and software developers.Secure communication hosters and software developers.Usenet / NNTP hosters and software developers.Cryptographers, cryptanalysts, cipher code makers and breakers.Writers of papers and preprints.Textual Criticism buffs and translators, including producers of papers and software. #Introduction #ActivityPub #Fediverse #Usenet #NNTP #InfoSec #Papers #Cryptography #Cryptology #Encryption #Bible #TextualCriticism #Antiquities #Translation

0
0
1
0
Polymarket Supply Chain Attack Drains $2.7 Million via Hijacked Third-Party Script Polymarket reports a supply chain attack after hackers hijacked the DNS records of its performance monitoring vendor, DebugBear, to inject a wallet-draining script. The malicious code exploited active user sessions to steal approximately $2.7 million from 726 wallets before the platform removed the script and initiated full refunds. **** #cybersecurity #infosec #incident #databreach
0
0
2
0
Hi infosec.exchange 👋 #introduction I'm Seven. In the early 2000s I was writing AIM "progs" in VB6: punters, clone loaders, bots. Learned security by poking at AOL's protocols before most of the rules existed. These days: C#, PHP, web security and AI tooling. I'll be posting about web security, old-school exploits vs. modern defenses, and internet history. Archive: https://sevlegend.com Code: https://github.com/seven305/aim-progs-archive #infosec #websecurity #appsec #retrocomputing
0
0
1
0
RE: https://mas.to/@markwyner/116184563372403595 Imagine trusting your privacy with a company who favors speed over integrity. A @protonprivacy@mastodon.social employee cautioned against releasing new code that wasn’t properly tested. Andy Yen responded to all Proton employees: “That’s bullshit and loser thinking. Of course it’s possible to be fast and secure. Stop thinking always of how to be slower, and focus more on how to be faster. Only losers think like that. Stop lovingly handcrafting all our code and use AI more.” Some of us keep warning folks to avoid Proton. Unfortunately, others, like trusted source @privacyguides@mastodon.neat.computer, ignore the red flags and recommend it anyway. If you use Proton, you’re at risk. https://www.404media.co/manifestos-fear-and-loser-thinking-inside-protons-ai-reckoning #Proton #Privacy #InfoSec #AndyYen #AI
Quoting
For anyone who still thinks Proton is all that: https://www.404media.co/proton-mail-helped-fbi-unmask-anonymous-stop-cop-city-protestor/ Many of us have been raising alarm bells because their CEO is a fascist boot licker. Some say that’s hot air, but he continues to fit the M.O. https://techstory.in/proton-mail-faces-backlash-over-claims-of-political-neutrality-amid-ceos-praise-for-republican-party/ https://mas.to/@markwyner/115199799549199535 https://lgbtqia.space/@alice/113830130669521824 Ditch Proton. You deserve better. #Proton #Privacy #InfoSec #FBI #ProtonIsNotYourFriend
Open quoted post
113
25
134
5
Hi infosec.exchange. I'm Jeff King, founder and president of AT-NET Services (@ATNETServices@infosec.exchange), an MSP and MSSP based in Charlotte, NC, in business since 1999. Most of my time now goes to CMMC: helping defense contractors scope their CUI, decide whether they need GCC High, and stay compliant after the assessment, not just pass it. I'll post about CMMC, NIST 800-171, M365 security and what running an MSP looks like from the inside. Glad to trade notes. #introduction #CMMC #MSP #infosec
0
0
1
0
Vultr must have the most stupid way of OTP management I've seen in a long while. You cannot delete an OTP token on your account if you do not have access to the OTP token. Let that sink in. If you try to delete a token from your Vultr account, you need to enter the OTP value of that token to be allowed to remove it. Then consider a scenario where you've lost access to a hardware token, or like if your mobile holding the token has been stolen. The same goes for backup codes. This is quite a huge security fail. Of course, it could be I'm just stupid and haven't understood the account management panel. #vultr #infosec #otp #totp #fail (Luckily, I was just unfortunate and deleted the Vultr OTP in my OTP manager - so the risk is manageable + I'm moving away from Vultr, now definitely completely)
0
0
0
0
Vultr must have the most stupid way of OTP management I've seen in a long while. You cannot delete an OTP token on your account if you do not have access to the OTP token. Let that sink in. If you try to delete a token from your account management, you need to enter the OTP value of that token to be allowed to remove it. Then consider a scenario where you've lost access to a hardware token, or like if your mobile holding the token has been stolen. The same goes for backup codes. This is quite a huge security fail. Of course, it could be I'm just stupid and haven't understood the account management panel. #vultr #infosec #otp #totp #fail (Luckily, I was just unfortunate and deleted the Vultr OTP in my OTP manager - so the risk is manageable + I'm moving away from Vultr, now definitely completely)
0
0
0
0
Vultr must have the most stupid way of OTP management I've seen in a long while. You cannot delete an OTP token on your account you do not have access to Let that sink in. If you try to delete a token from your account management, you need to enter the OTP value of that token to be allowed to remove it. Then consider a scenario where you've lost access to a hardware token, or like if your mobile holding the token has been stolen. The same goes for backup codes. This is quite a huge security fail. Of course, it could be I'm just stupid and haven't understood the account management panel. #vultr #infosec #otp #totp #fail (Luckily, I was just unfortunate and deleted the Vultr OTP in my OTP manager - so the risk is manageable + I'm moving away from Vultr, now definitely completely)
0
0
0
0