#cisa
63 posts · Last used 5d
#hackers have begun exploiting a critical #Brotli #vulnerability known as #Node2Shell, #Broccoli2Shell, and #HTTP2Shell.
https://nvd.nist.gov/vuln/detail/cve-2026-111497
#infosec #security #cisa #exploit
U.S. #CISA adds Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog
https://securityaffairs.com/199891/hacking/u-s-cisa-adds-citrix-netscaler-flaws-to-its-known-exploited-vulnerabilities-catalog.html
#securityaffairs #hacking
U.S. #CISA adds #WordPress flaw to its Known Exploited Vulnerabilities catalog
https://securityaffairs.com/199790/security/u-s-cisa-adds-wordpress-flaw-to-its-known-exploited-vulnerabilities-catalog.html
#securityaffairs #hacking
📰 CISA & FBI Warn of Third-Party Risks to Industrial Control Systems
CISA & FBI issue joint guidance on securing critical infrastructure from third-party ICS integrator risks. The advisory stresses least privilege, robust contracts, and secure remote access monitoring. #ICS #OTsecurity #CISA #SupplyChain
🔗
Replying to
“For them to come in five weeks before the election, yeah, nice effort,” said Nevada’s Democratic Secretary of State Cisco Aguilar, who added that he would have liked to see the federal government provide more funding for #cybersecurity, rather than Nevada taxpayers having to pay for it.
#Trump #ElectionInterference #law #CISA
Replying to
Homeland Security Secretary Markwayne Mullin had originally promised to release the plan by mid-August as part of the #Trump administration’s move to kickstart #election security assistance after a hiatus. He announced the plan at the same time he threatened election officials for not cooperating with the administration’s preferred methods to hunt down noncitizen voting, a phenomenon that research shows is extremely rare.
#ElectionInterference #law #CISA
Replying to
The #US #Cybersecurity & Infrastructure Security Agency, which is housed under DHS, has since its founding in 2018 helped warn state & local #election officials about potential threats from foreign governments.
But #CISA, as it’s known, was largely absent from that role in last year’s elections after the #Trump admin dismantled much of its role in election security.
#ElectionInterference #law
Replying to
The #Trump admin cut some 1,000 employees from #CISA & slashed $10 million from two #cybersecurity initiatives, including one dedicated to helping state & local #election officials.
CISA has also gone the entirety of Trump’s second term without a Senate-confirmed director, instead cycling through a series of acting leaders.
#ElectionInterference #law
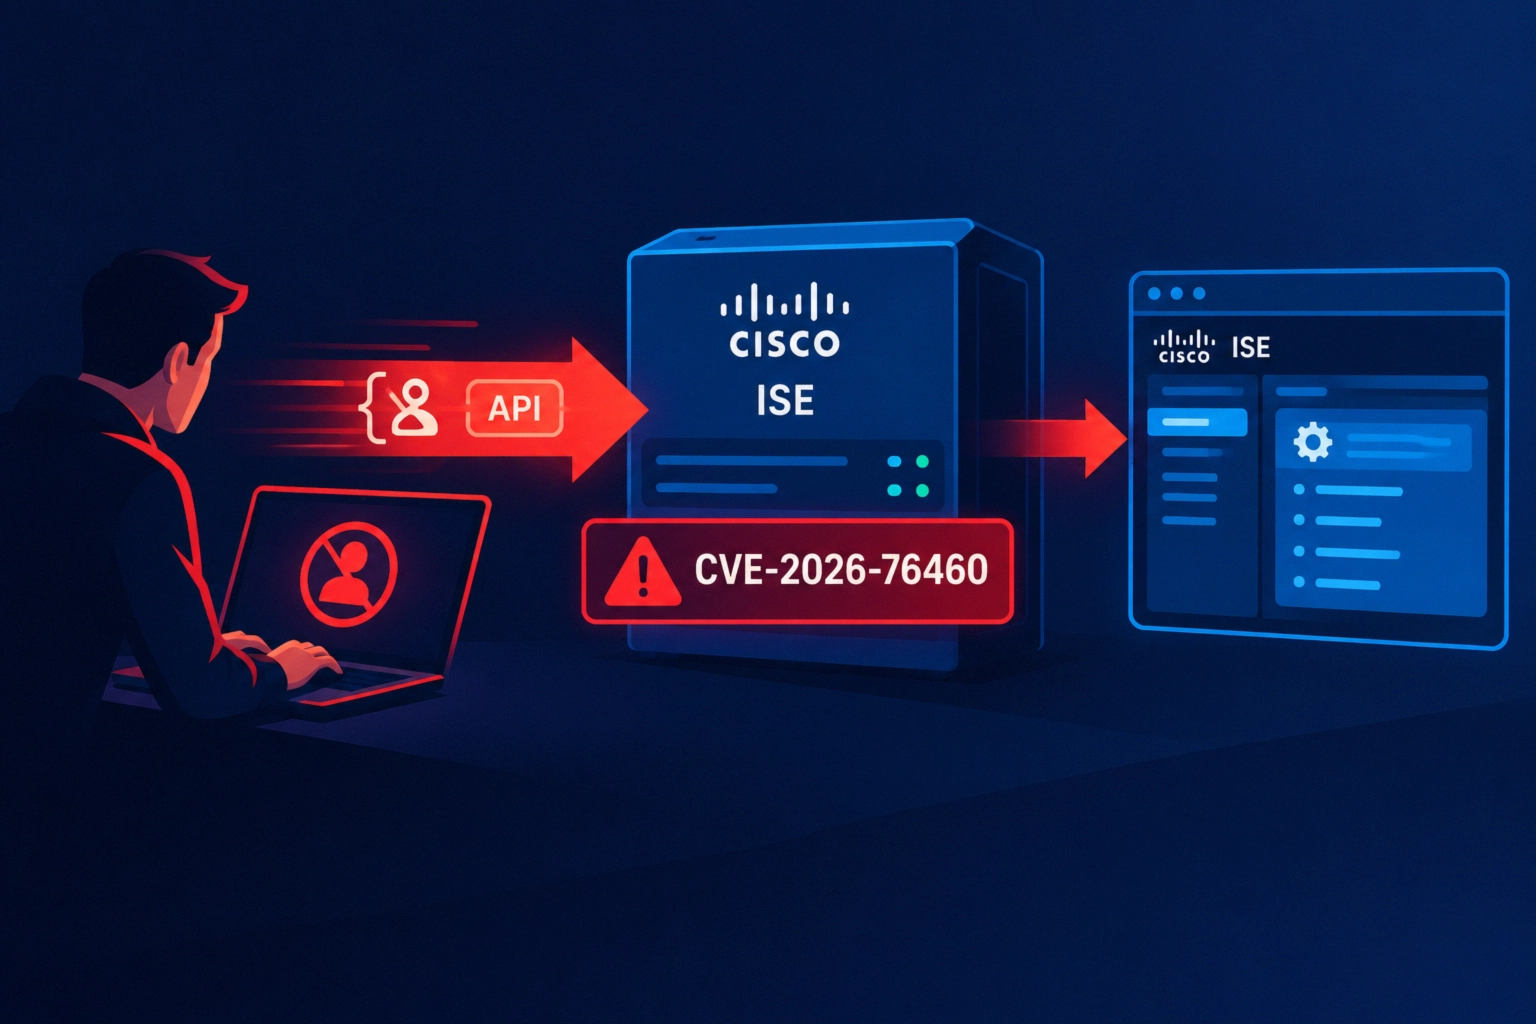
CVE-2026-76460: Cisco ISE authentication bypass with CVSS 10.0
🔗 https://cybersecurefox.com/en/cve-2026-76460-cisco-ise-authentication-bypass-cvss-10-0
#CVE-2026-76460 #Cisco #ISE #authentication #bypass #CVSS #10.0 #CISA #KEV
U.S. #CISA adds Linux Kernel flaws to its Known Exploited Vulnerabilities catalog
https://securityaffairs.com/199430/security/u-s-cisa-adds-linux-kernel-flaws-to-its-known-exploited-vulnerabilities-catalog-2.html
#securityaffairs #hacking
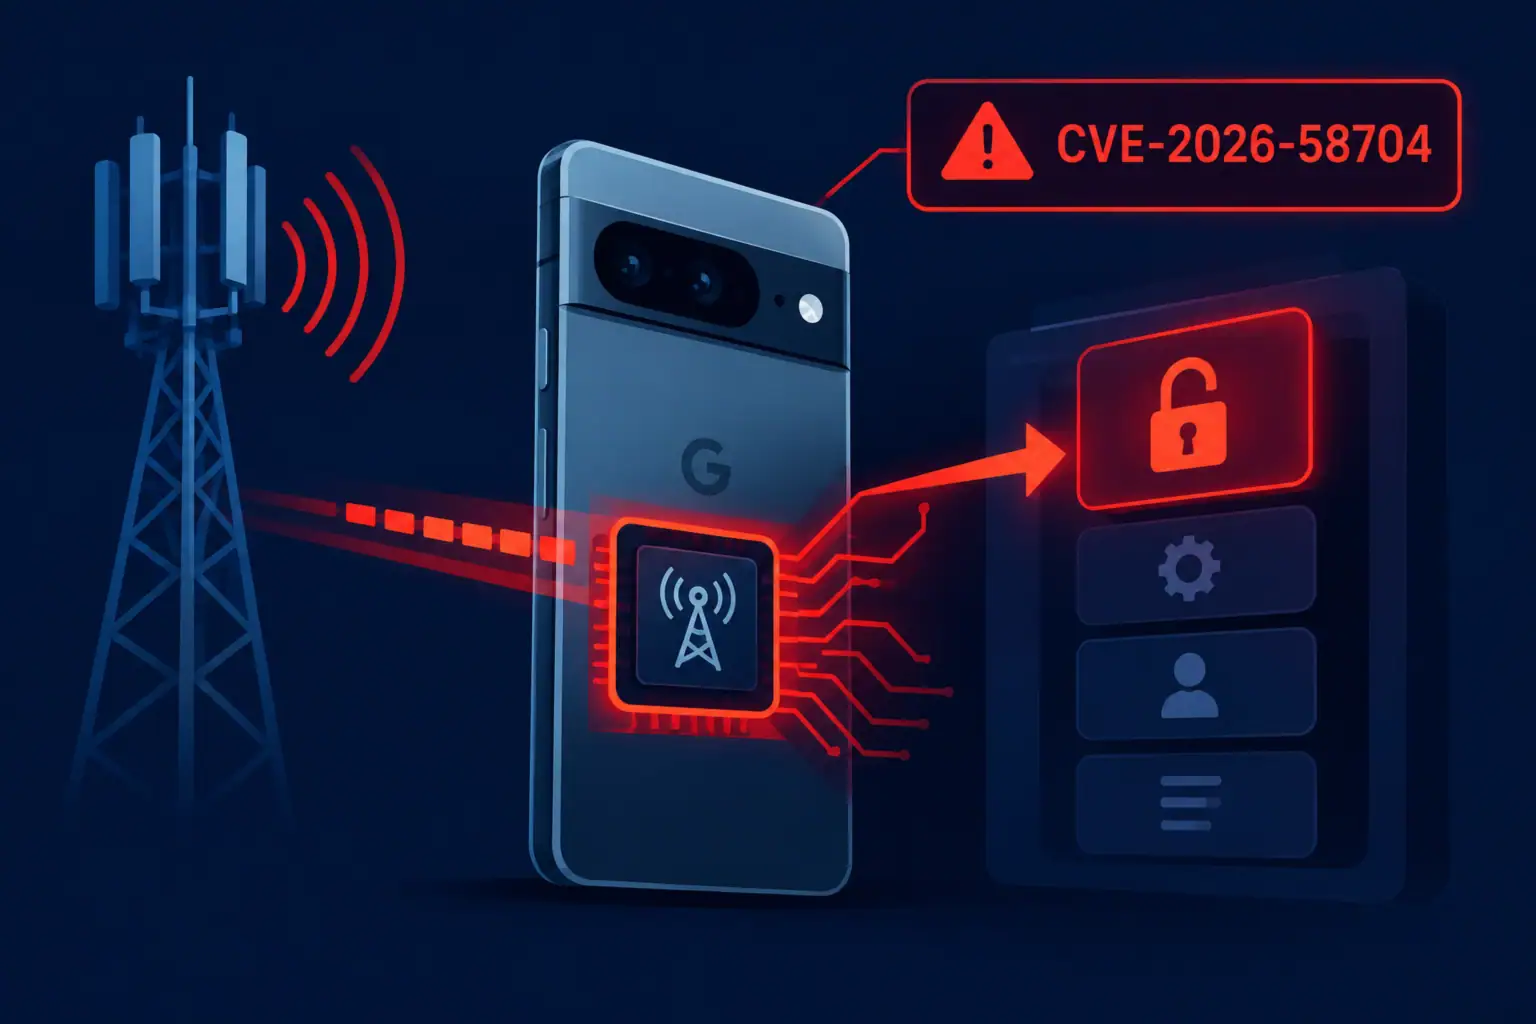
CVE-2026-58704: Pixel modem vulnerability added to CISA KEV catalog
🔗 https://cybersecurefox.com/en/cve-2026-58704-pixel-modem-privilege-escalation-cisa-kev
#CVE-2026-58704 #Google #Pixel #Cellular #Modem #CISA #KEV #privilege #escalation
Learn why CISA added GitLab CVE-2026-85706 to the Known Exploited Vulnerabilities catalog. Discover how this CVSS 10 flaw allows remote secret extraction.
#GitLab #CVE202685706 #CISA #CyberSecurity #Vulnerability
U.S. #CISA adds #Cisco Secure Email Gateway flaw to its Known Exploited Vulnerabilities catalog
https://securityaffairs.com/199156/security/u-s-cisa-adds-cisco-secure-email-gateway-flaw-to-its-known-exploited-vulnerabilities-catalog.html
#securityaffairs #hacking
#CISA confirms hackers targeted over 100 US #water systems during July
https://techcrunch.com/2026/08/26/cisa-confirms-hackers-targeted-over-100-us-water-systems-during-july/
#cybersecurity #infrastructure #utilities
CVE-2026-8037: CISA Adds Progress LoadMaster Flaw to KEV
🔗 https://cybersecurefox.com/en/cve-2026-8037-progress-kemp-loadmaster
#cve-2026-8037 #progress #kemp #loadmaster #cisa #kev #command #injection #exploited #vulnerability
U.S. #CISA adds a #Progress #LoadMaster flaw to its Known Exploited Vulnerabilities catalog
https://securityaffairs.com/196863/hacking/u-s-cisa-adds-a-progress-loadmaster-flaw-to-its-known-exploited-vulnerabilities-catalog.html
#securityaffairs #hacking
CISA Adds Three Actively Exploited Flaws to KEV Catalog
🔗 https://cybersecurefox.com/en/cisa-adds-langflow-tomcat-n-central-kev
#cisa #kev #catalog #langflow #rce #apache #tomcat #encryption #bypass #n-able #n-central #authentication #bypass
CVE-2026-18577: N-able N-central Auth Bypass Exploited
🔗 https://cybersecurefox.com/en/cve-2026-18577-n-able-n-central-auth-bypass
#CVE-2026-18577 #N-able #N-central #CISA #KEV #authentication #bypass #RMM #security
TeamCity vulnerability CVE-2026-63077 enables unauthenticated remote code execution. CISA added it to the KEV catalog amid active exploitation.
#TeamCity #CVE202663077 #RCE #CISA #KEV #CyberSecurity
CISA added three bugs to its KEV list. An N-able N-central authentication bypass is exploited in the wild to deploy RMM tools. Patch by August 7.
#Nable #Ncentral #CISA #KEV #CVE202618556 #ExploitedInTheWild #RMM #Langflow #ApacheTomcat #CyberSecurity #InfoSec