#lpe
12 posts · Last used Aug 06
Another KVM guest escape to root (read LPE) just got disclosed https://zapscape.io
I'll log my findings in replies
#linux #lpe #zapscape
Details and proof-of-concept exploit code for CVE-2026-50343 are now public. The Windows privilege escalation flaw hands standard users SYSTEM privileges.
#CVE202650343 #Windows #PrivilegeEscalation #LPE #InfoSec
🚨 RefluXFS (CVE-2026-64600) has been identified as a notable vulnerability.
In the Linux kernel, the following vulnerability has been resolved:
xfs: resample the data fork mapping after cycling ILOCK
RefluXFS is a local privilege escalation vulnerability in the Linux kernel's XFS filesystem copy-on-write path. It allows local users to overwrite protected files and gain root access.
ℹ️ Additional details on ZEN SecDB https://secdb.nttzen.cloud/updates/1d26eb14-ce27-4846-a8ce-bae087fb1e46/refluxfs-vulnerability
#infosec #refluxfs #linux #kernel #xfs #lpe
#nttdata #zen #secdb
🤖 CVE-2026-8933 (CVSS 7.8): LPE in Ubuntu snap-confine gives root on default desktop installs (24.04, 25.10, 26.04). Researchers published details — unprivileged users can escalate to root.
🔗 https://thehackernews.com/2026/07/ubuntu-snap-confine-flaw-could-give.html
#CVE #Ubuntu #LPE #CyberSec
Dirty Clone – kolejny sposób na roota pod Linuksem https://sekurak.pl/dirty-clone-kolejny-sposob-na-roota-pod-linuksem/ #Aktualnoci #Eskalacja #Hacking #Kernel #Linux #Localroot #Lpe #Pagecache
Dirty Clone – kolejny sposób na roota pod Linuksem
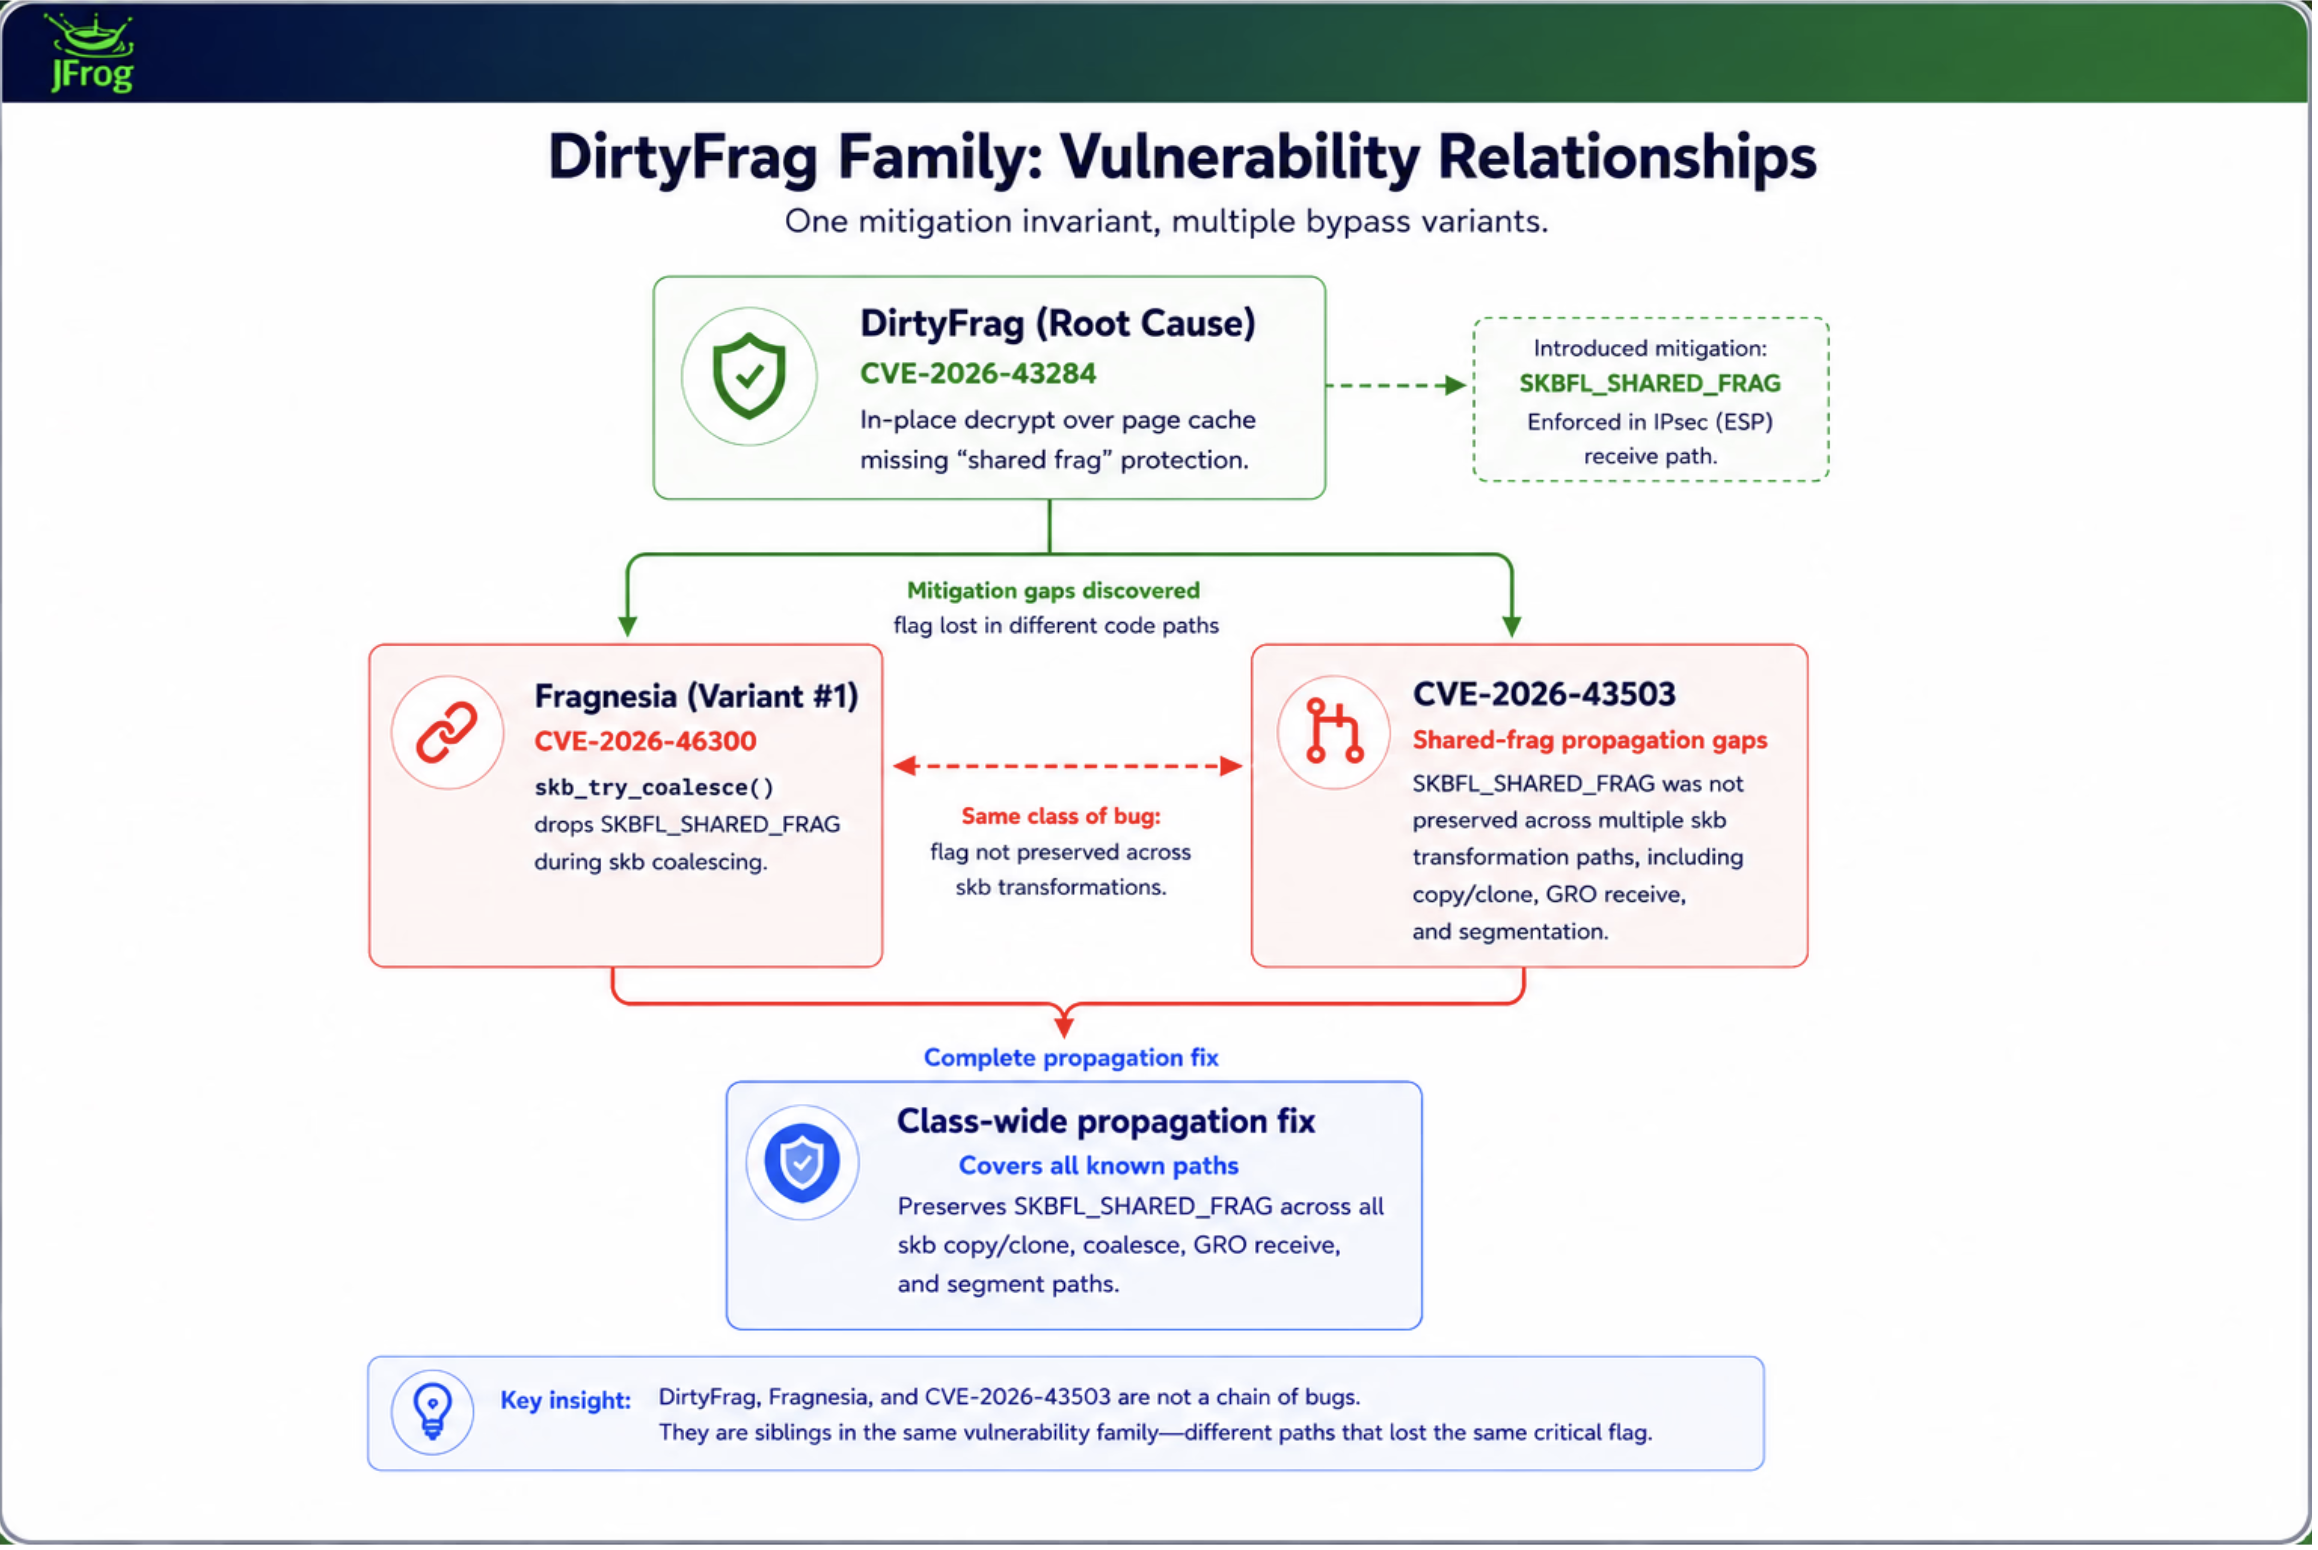
Nie tak dawno pisaliśmy o serii podatności Dirty Frag występujących w większości nowoczesnych dystrybucji Linuksa. I choć mogłoby się wydawać, że deweloperzy naprawili błędy, to najnowsze badania pokazują, że problem nie został jednak wyeliminowany. W jądrze pozostała bowiem niezałatana luka, którą badacze z JFrog ochrzcili mianem Dirty Clone (CVE-2026-43503). Podobnie...
#Aktualności #Eskalacja #Hacking #Kernel #Linux #LocalRoot #Lpe #PageCache
🚨 DirtyClone (CVE-2026-43503)
In the Linux kernel, the following vulnerability has been resolved:
net: skbuff: propagate shared-frag marker through frag-transfer helpers
ℹ️ Additional info on ZEN SecDB https://secdb.nttzen.cloud/updates/9a1828d5-6607-419b-b475-622a6c135aae/dirtyclone-vulnerability
#nttdata #zen #secdb
#infosec #dirtyclone #linux #lpe #cve202643503
#LPE — Local Privilege Escalation. A class of vulnerabilities that need a local user account on the target machine to reach higher levels of privilege, up to superuser/root
#RCE — Remote Code Execution. A class of vulnerabilities that can be exploited over unprivileged network connections, giving the attacker privileged access to the target machine.
#CopyFail, #DirtyFrag are LPEs that affect Linux systems. LPEs are typically harder to exploit than RCEs.
Hope this helps to avoid Clickbait.
Dirty Frag – kolejna metoda na root’a pod Linuxem
Pamiętacie Dirty Pipe? Łataliście ostatnio Copy Fail? Pasy zapięte? Nie? To niedobrze, bo kilka godzin temu pojawiła się nowa podatność określona mianem Dirty Frag. W ramce poniżej znajduje się tymczasowe rozwiązanie mające na celu wyłączenie niebezpiecznych modułów. Jest to luka klasy LPE (local privilege escalation), która pozwala na podniesienie uprawnień...
#Aktualności #EskalacjaUprawnień #Kernel #Linux #LocalRoot #Lpe #Pipe
https://copy.fail/
Local Privilege Escalation in every Linux kernel since 2017
Hopefully no one is sitting on a low-privilege RCE...
#linux #security #rce #lpe #cve #CVE202631431
You've seen all posts