#cve

381 posts · Last used 6d

There isn't an easy exploit for this PHP vulnerability I came across the link via https://mastodon.social/@CuratedHackerNews/117481600704689796 Last time I touched php it was ~20 years ago and maybe for a month. Could someone with actual php understanding weigh in? Somehow, somewhere between the lines, my understanding was that there have been observances of the vuln being used in the wild before the 14 UTC. And that wasn’t from reading news sites
0
5
0
0

📣 Announcing the immediate availability of:

  • PHP 8.2.35
  • PHP 8.3.36
  • PHP 8.4.27
  • PHP 8.5.12

‼️ These address the following critical security issues:

  • Remote Code Execution via Out of Memory corruption (CVE-2026-109618)
  • Remote Code Execution via Stale Global State (CVE-2026-109619)

📝 https://www.php.net/ChangeLog-8.php 🎁 https://www.php.net/downloads?source=Y :windows8: Windows: https://www.php.net/downloads.php?os=windows

Read more: https://www.php.net/archive/2026.php#2026-10-21-5

#PHP #Release #Security #CVE

654
16
904
19

I audited #OpenReception, a recently released open-source appointment booking platform. Found and reported 16 vulnerabilities, now 16 CVEs assigned.

4 critical:

  • WebAuthn passkey injection → account takeover
  • tenant admin self-promotes to GLOBAL_ADMIN
  • unauth GLOBAL_ADMIN account creation
  • staff crypto poisoning breaks the E2E recipient directory

rest: info disclosure, stored XSS, auth and IDOR bugs, all patched before public disclosure.

https://moltenbit.net/disclosures/

#infosec #security #CVE

2
0
0
1

[🚨 #MediaWiki vulnerable extension]

If you are running a MediaWiki instance with Extension:External_Data < v3.7, your instance is vulnerable to arbitrary file loading and #RemoteCodeExecution.

The vulnerability was apparently publicly known since August, but due to the lack of communication, instance admins learned about it due to that vulnerability being exploited en masse.

If you know and like a MediaWiki instance, you can check their Special:Version page to see if they are using the External_Data extension to warn them.

More info:

#infosec #wikipedia #wikidata #adminsys #security #CVE #pwned

5
6
7
0
🤖 CVE-2026-86950: out-of-bounds write in Apple CoreGraphics. A maliciously crafted file can lead to arbitrary code execution. Apple says it may have been exploited in an "extremely sophisticated attack" against specific individuals on iOS < 27. Fixed in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1 and Sequoia 15.8.1. 🔗 https://thehackernews.com/2026/09/apple-patches-coregraphics-flaw.html #CVE #Apple #Exploit #CyberSec
0
0
1
0
🤖 Apple patched CVE-2026-86950, an out-of-bounds write in CoreGraphics affecting older iOS/iPadOS/macOS versions. Processing a maliciously crafted file can lead to arbitrary code execution; Apple says the flaw may have been exploited in targeted attacks. 🔗 https://thehackernews.com/2026/09/apple-patches-coregraphics-flaw.html #CVE #Apple #InfoSec #CyberSec
1
0
2
0
Another day, another critical vulnerability in an edge device. We’ve analysed the CVE-2026-88771, one of the many vulnerabilities disclosed by Citrix recently, based on observed exploitation attempts, and set out what we learned and key takeaways. 🔍🔒 If you’re managing Citrix infrastructure, now’s the time to check for compromise! https://www.cert.europa.eu/blog/taking-execute-logging-a-bit-too-literally-cve-2026-88771 #cybersecurity #cve-2026-88771 #vulnerability
9
3
15
0
Replying to
CISA working on a Sunday: Citrix NetScaler zero-days CVE-2026-88771 and CVE-2026-887712 were added to the Known Exploited Vulnerabilities (KEV) Catalog, based on evidence of active exploitation. https://www.cisa.gov/news-event/alerts/2026/09/27/cisa-adds-two-known-exploited-vulnerabilities-catalog #KEV #Citrix #NetScaler #zeroday #CVE
1
3
2
0
Krytyczna luka w Linux KVM na ARM64. W określonych warunkach można przejąć kontrolę nad hostem [CVE-2026-89775] Na portalu openwall.com badacz bezpieczeństwa Hyunwoo Kim opublikował wpis zawierający szczegóły krytycznej podatności w podsystemie KVM (Kernel-based Virtual Machine) dla architektury ARM64 w jądrze Linuxa. Luka oznaczona identyfikatorem CVE-2026-89775 umożliwia ucieczkę z maszyny wirtualnej i uzyskanie dostępu do pamięci hosta. Może to prowadzić do przejęcia kontroli nad systemem (hypervisorem).  TLDR:... #Aktualności #Cve #Kvm #Linux #Rce
2
0
3
0
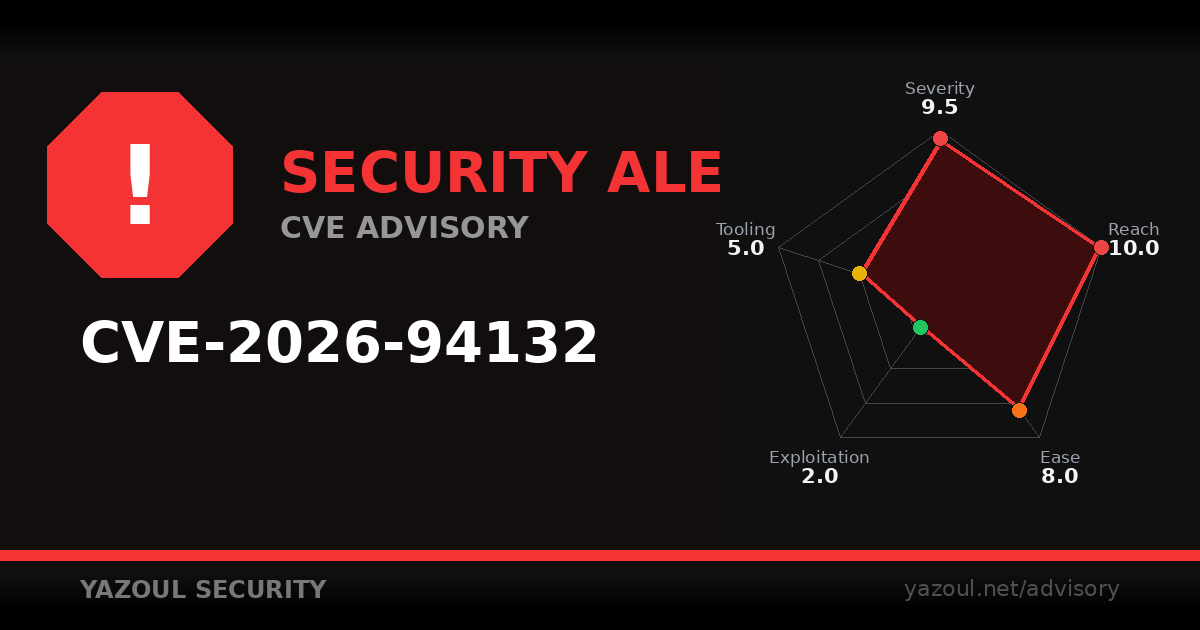
🔴 New security advisory: CVE-2026-94132 affects multiple systems. • Impact: Remote code execution or complete system compromise possible • Risk: Attackers can gain full control of affected systems • Mitigation: Patch immediately or isolate affected systems Full breakdown: https://www.yazoul.net/advisory/cve/cve-2026-94132-acymailing-rce-unauthenticated-email-upload-poc by Yazoul AI #CVE #PatchNow #InfoSecCommunity
0
0
0
0