#redteam

66 posts · Last used 18d

OffSeq is an European offensive security company. We do pentesting, red teaming, OT/ICS and critical infrastructure security, and NIS2/DORA work across the EU. Here we post our research: vulnerability disclosures (latest in Latvian and Estonian eID software and X-Road), monthly Mirage honeypot field reports and open-source tools. Open to collaboration, DMs are open. https://offseq.com/en/ #Introduction #InfoSec #PenTest #RedTeam #ThreatIntel #OffensiveSecurity
1
0
3
0
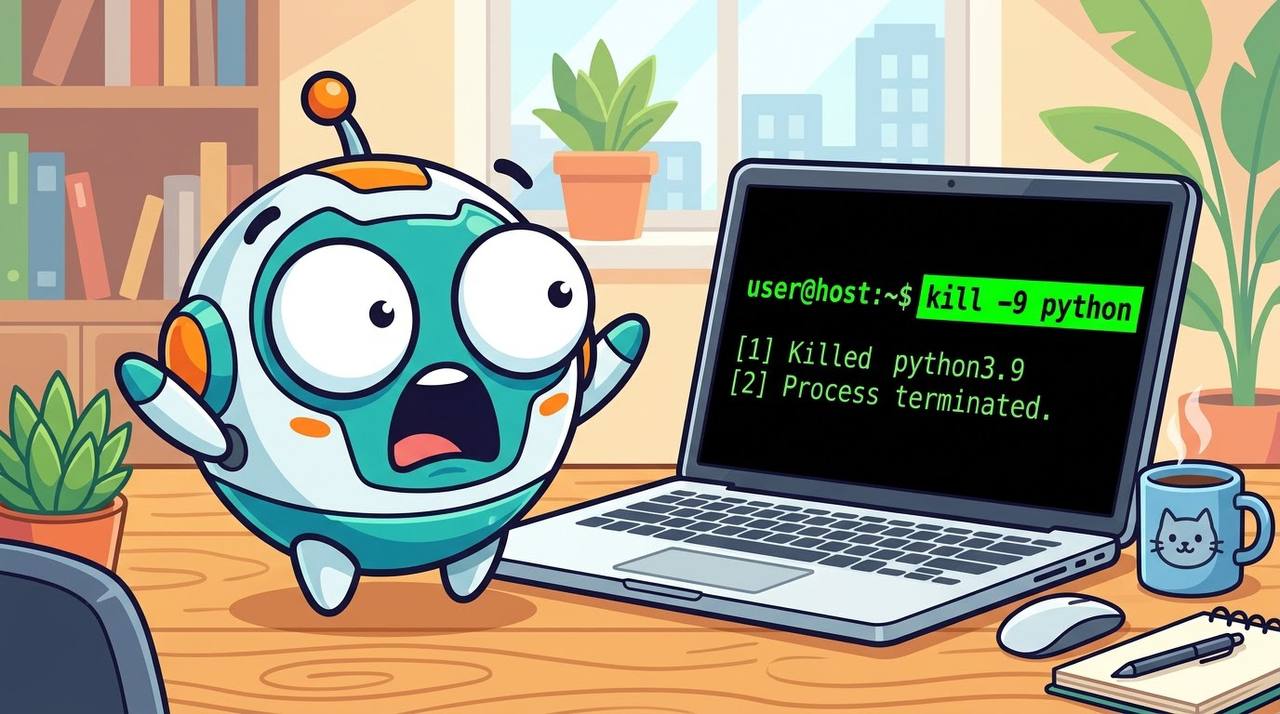
My local 7B safety judge flags "kill a Python process" as a violent crime — while a hand-written regex scores it 0.0% correctly. Full contrast-pair table + setup (Qwen 7B, llama.cpp, temp 0): https://amirulcyber.com/2026/09/17/local-7b-homonym-failures/ #AISecurity #LLM #RedTeam
2
0
0
0
Replying to
New blog post! I recently got to use both of the tools I published on Codeberg (Axmar and Tessera) during an engagement, and so I decided to make a brief writeup as a case study of what these tools can do. https://ti-kallisti.com/tales/schedule.html #infosec #pentesting #redteam #redteaming #Microsoft #ActiveDirectory #MSSQL
2
2
1
0
🎥 A session from BSides Luxembourg 2026 is now available to watch! 🟣🤖 𝗚𝗢𝗢𝗗𝗕𝗬𝗘 𝗣𝗨𝗥𝗣𝗟𝗘 𝗧𝗘𝗔𝗠, 𝗛𝗘𝗟𝗟𝗢 𝗣𝗨𝗥𝗣𝗟𝗘 𝗕𝗢𝗧𝗦 🛡️⚔️ Patrick Mkhael https://pretalx.com/bsidesluxembourg-2026/speaker/WHMGFD/ Ralph El Khoury https://pretalx.com/bsidesluxembourg-2026/speaker/X9QCJN/ Watch Patrick Mkhael and Ralph El Khoury's session, recorded live at the Digital Learning Hub during BSides Luxembourg 2026. https://archive.org/details/BSidesLuxembourg2026/d1+t2+08+Goodbye+Purple+Team%2C+Hello+Purple+Bots+-+Patrick+Mkhael+and+Ralph+El+Khoury.mkv "smartCard-inline" #BSidesLuxembourg2026 #CyberSecurity #PurpleTeam #RedTeam #BlueTeam #AI
2
0
3
0
🛡️ USecVisLib — open-source Universal Security Visualization Library. Attack trees, attack graphs, STRIDE threat models, MAESTRO AI-agent threat modeling, binary viz & more. Python + FastAPI + Vue 3. Apache 2.0. https://github.com/vulnex/usecvislib #infosec #threatmodeling #opensource #redteam #blueteam
1
0
0
0
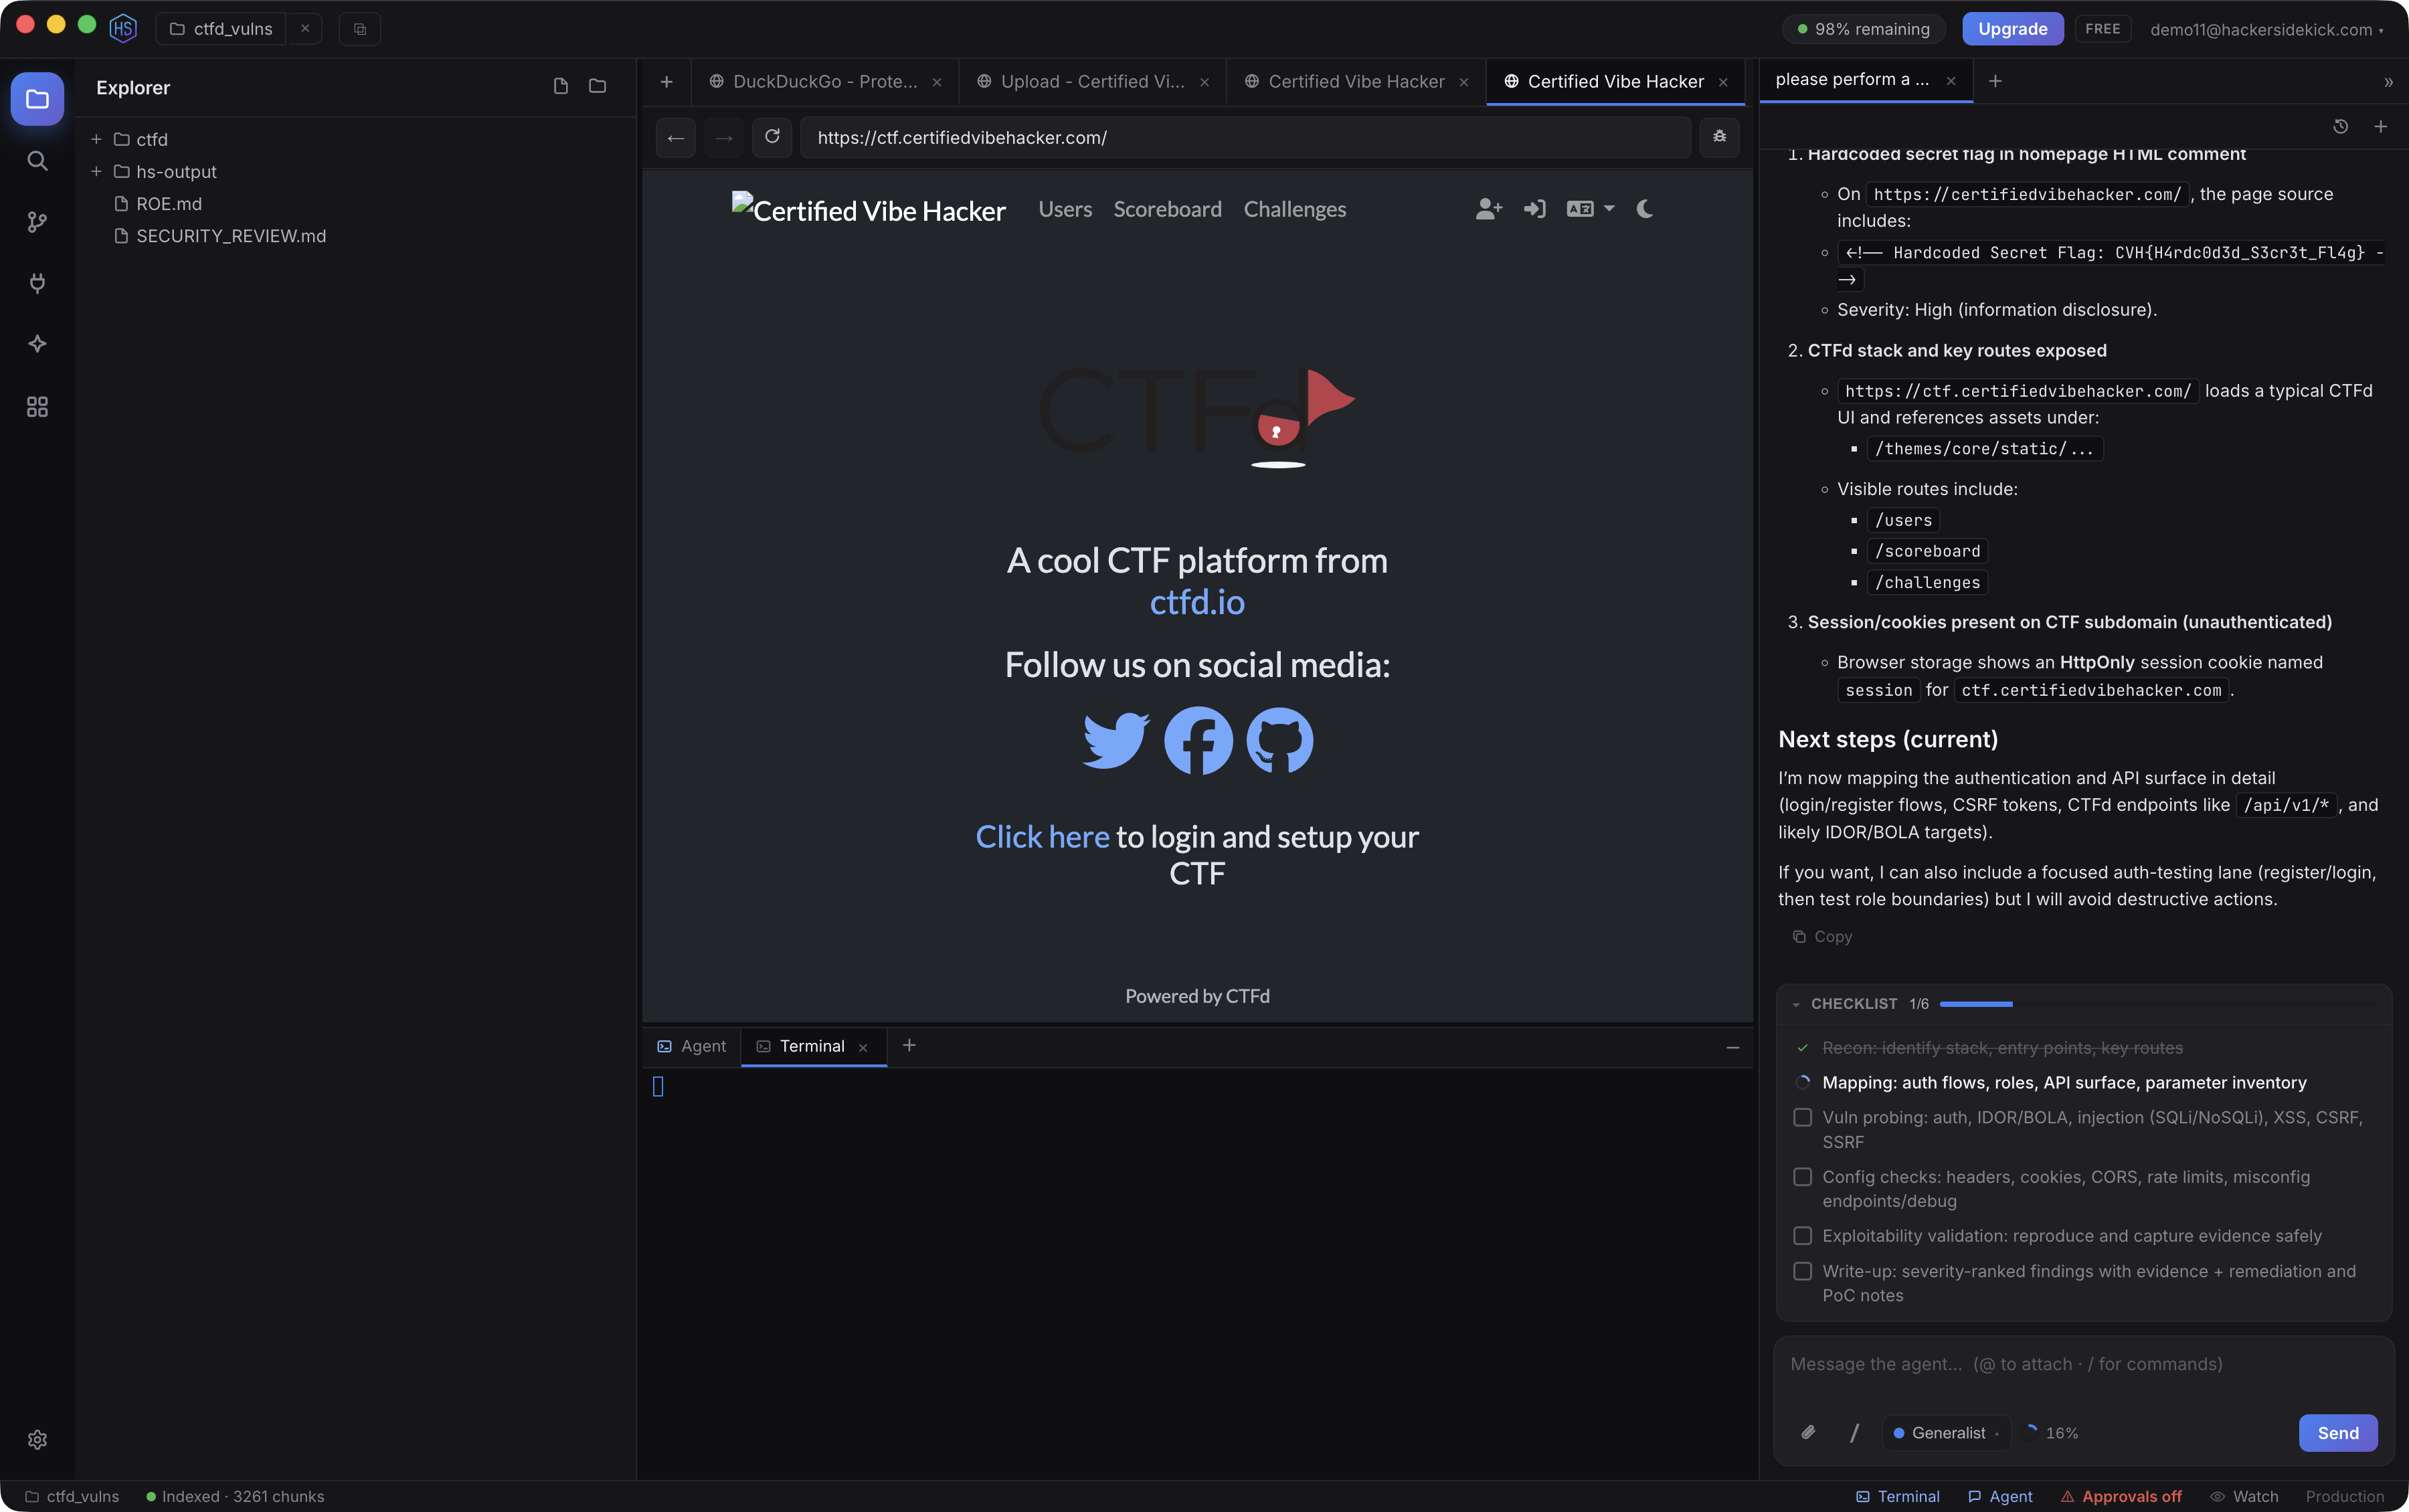
The Agentic Workbench for Cybersecurity has been rebuilt from the ground up. Our biggest update ever! Hacker Sidekick actually does the work in one window where the analysis lives next to the execution. What the rebuild unlocks: An agent that drives a real browser. Not screenshots of a browser, a real sandboxed Chromium it operates for you. It inspects the DOM, pulls full request and response bodies, reads storage and cookies including HttpOnly, walks login flows, and intercepts traffic proxy-style to hold, modify, or block requests. 77 tool integrations that pull your critical data into one place. Threat intel, SIEM, EDR, and ticketing, plus a built-in intel server with MITRE ATT&CK, NVD, VirusTotal, Shodan, Censys, and Exploit-DB out of the box with no key. Watch mode, a second set of eyes. Toggle it and a passive monitor observes your terminal and browser and surfaces brief advice: a missed step, forgotten cleanup, a scope concern. It only advises. It has no tools of its own and never acts. Because it is one integrated environment instead of a browser tab bolted onto a chat, all of this is faster, more powerful, and more connected. The agent plans and asks, security modes and approval gates keep it in bounds, and every command it runs is visible. Nothing happens off-screen. That is the integrated hacking environment. Full tour: https://hackersidekick.com/inside-hacker-sidekick-desktop-feature-tour.html?utm_source=linkedin&utm_medium=social&utm_campaign=desktop_feature_tour #cybersecurity #infosec #pentesting #hackersidekick #AI #dfir #redteam #threatintelligence
0
0
0
0