#firmware
29 posts · Last used Sep 25
New post: Open Tabs CW39/2026
This week's links cover the fragility of US-based infrastructure, smart fridge firmware, AI-generated slop, journald, and the art of asking good questions.
https://stoeps.de/posts/2026/open-tabs-cw39/
Reply to this toot to leave a comment - replies will appear below the article automatically.
#omb #ai #ask #eu #firmware #fridge #genie #iot #journald #question #samsung #schneier #slop #systemd #us
osmose firmware update 2.3 - overview
https://www.matrixsynth.com/2026/09/osmose-firmware-update-23-overview.html
#Synthesizers #MusicTech #Firmware
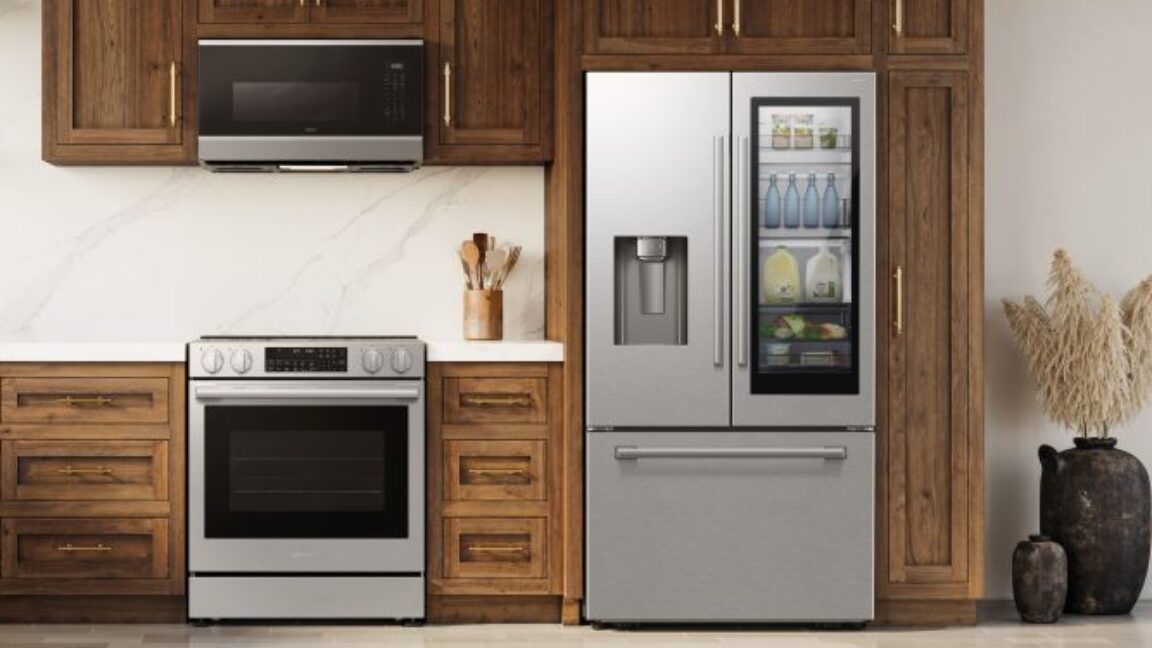
Owners mourn spoiled food after #firmware update #bricks #Samsung smart fridges
Some Samsung smart #fridges stopped working on Tuesday due to a firmware update.
#Korean outlets were the first to report the problems, which affect Samsung’s #Bespoke #AI line of fridges. Star News Korea, per a Google-provided translation, said that most of the affected devices were four-door fridges from 2024 or later.
Affected fridges “suddenly lost power and stopped functioning immediately after” trying to issue a firmware update through #SmartThings,
#Smartfridge
Keychron announced "ZGM", open-source firmware for gaming mice https://www.gamingonlinux.com/2026/08/keychron-announced-zgm-open-source-firmware-for-gaming-mice/
#OpenSource #Firmware #PCGaming #Gaming #Keychron
S2400 gets automation.. (beta firmware)
https://www.matrixsynth.com/2026/07/s2400-gets-automation-beta-firmware.html
#Synthesizers #MusicTech #Firmware
----------------
🛠️ Tool
===================
VulHunt Community Edition is an open-source vulnerability hunting framework developed by Binarly's Research team. It is designed to help security researchers identify vulnerabilities in software binaries and UEFI firmware. Built on top of Binarly's Binary Analysis and Inspection System (BIAS), the tool provides a flexible environment for analyzing binaries. It integrates with the Binarly Transparency Platform (BTP) for large-scale vulnerability management, hunting, and triage capabilities.
Key Features
• Open Source Engine: The Community Edition provides the core VulHunt engine for free, facilitating community-developed rulepacks and integrations.
• Multiple Loaders: Supports scanning single binary files (component), BA2 archives (ba2), and Binary Ninja databases (bndb).
• MCP Server Mode: Can run as a Model Context Protocol (MCP) server for integration with AI assistants. By default, it starts a streaming HTTP server with SSE transport at http://127.0.0.1:8080
• Output Formats: Supports standard JSON output, human-readable formatting (--pretty), streaming JSONL messages (--stream), and Zstandard compression (--compress).
Technical Implementation
The framework is built in Rust and can be compiled using cargo-make. It requires a patched version of LuaJIT for static building. On Windows, it uses msvcbuild.bat to compile LuaJIT. The tool accepts directories containing auxiliary data, rules, and modules via command line arguments or environment variables (BIAS_DATA, BIAS_VULHUNT_RULES, BIAS_VULHUNT_MODULES).
Use Cases
• Automated scanning of firmware images and software binaries for known and unknown vulnerabilities using custom rulepacks.
• Integrating binary analysis capabilities directly into AI assistant workflows via the MCP server interface.
• Large-scale vulnerability triage when combined with the Binarly Transparency Platform.
Limitations
Building the tool without cargo-make requires manual setup of a patched LuaJIT, which might introduce friction for some environments. Binary Ninja database scanning requires enabling the bndb feature at build time.
🔹 vulhunt #binarly #uefi #firmware #tool
🔗 Source:
Nach der Migration ist vor der Migration? — In den vergangenen Jahren war die Migration anderer Communities auf die Firmware und Infrastruktur des 4830.org e. V. ein nicht unwichtiges Thema. Aber je mehr die Zeit fortschreitet, ist die Notwendigkeit, von Gluon v2021.1 auf Gluon v2023.1 aktualiseren zu können, ein wachsender Showstopper.
https://4830.org/2026/07/29/nach-der-migration-ist-vor-der-migration/ #Firmware
🔧 kendallgoto/ilo4_unlock
A toolkit for patching HPE's iLO 4 Firmware with access to previously inaccessible utilities
Patches HPE iLO 4 firmware to unlock SSH commands for fan control, temperature monitoring, and system health on servers like DL380p Gen8/9
⭐ Stars: 556
📅 Last Update: Jul 28, 2026
https://github.com/kendallgoto/ilo4_unlock
#selfhosted #homelab #selfhost #selfhosting #opensource #firmware #ilo4
Replying to
@MugsysRapSheet@mastodon.social @Orb2069@mastodon.online
In 1984 the GNU Project set out to make it possible to operate a computer in freedom--to operate it without any non-free software that would deny the user's freedom
At the time, the obstacle to this was simply the operating system. A computer won't run without an operating system, but all the modern operating systems of 1983 were proprietary, user-subjugating software. There was no way to use modern computers in freedom. We set out to change the situation by developing a free software operating system, called GNU.
When the kernel Linux became free software in 1992, it filled the last gap in GNU. The combined GNU/Linux operating system achieved our goal: you could install it in a bare PC, and run the computer without any installed non-free software.
Strictly speaking, there was a non-free program in that computer: the BIOS. But that was impossible to replace, and by the same token, it didn't count.
The BIOS was impossible to replace because it was stored in ROM: the only way to to put in a different BIOS was by replacing part of the hardware. In effect, the BIOS was itself hardware--and therefore didn't really count as software.
#Firmware #Flash #CMOS #CoreBoot #FreeSoftware #LibreBoot #BIOS
Boosted by @GroupNebula563@mastodon.social
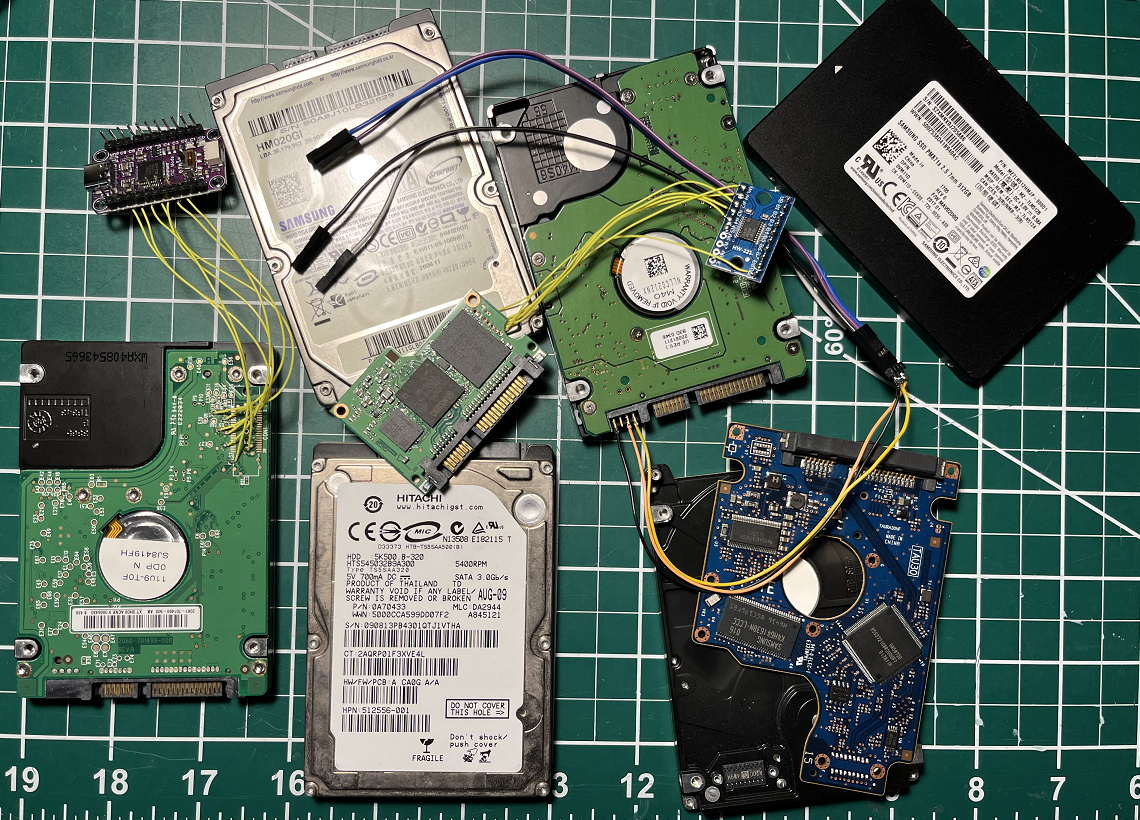
From spinning platters to firmware internals: a fascinating look at how hard drives really work. If you're into embedded systems, firmware analysis, or hardware hacking, this is worth your time
https://icode4.coffee/?p=1465
#embedded #firmware #JTAG
Kein bekannter Fehler bei uns im Update-Prozeß — Anfang Juli 2026 triggerte uns ein Beitrag der Münchner Kollegen über einen »bekannten Fehler« beim Firmware-Update — wie bitte?
https://4830.org/2026/07/19/kein-bekannter-fehler-bei-uns-im-update-prozess/ #Firmware
Ungeschützte Wechselrichter: Hoymiles verspricht Update
Angreifer können durch Sicherheitslücken in Hoymiles-Wechselrichtern die Geräte aus der Ferne lahmlegen. Ein Update soll das ändern.
https://www.heise.de/news/Ungeschuetzte-Wechselrichter-Hoymiles-verspricht-Update-11365046.html?wt_mc=sm.red.ho.mastodon.mastodon.md_beitraege.md_beitraege&utm_source=mastodon
#Firmware #IT #Security #Updates #news
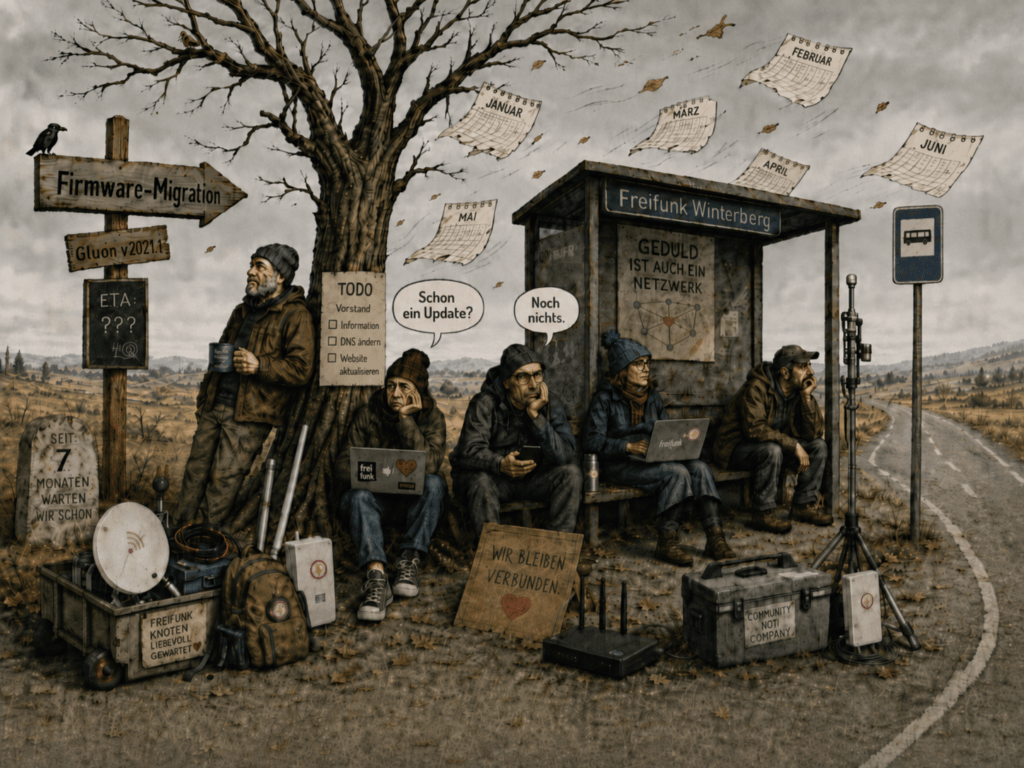
Freifunk Winterberg: Zug abgefahren — Wenn man sich die Zusammenfassung des Freifunk-Winterberg-Hilfeersuchen-Threads ansieht ahnt man, daß das Thema durch, der Zug abgefahren, das Schiff losgesegelt ist.
https://4830.org/2026/07/15/freifunk-winterberg-zug-abgefahren/ #Firmware
one of the things a surprising amount of people forget when they receive a new (second hand) hardware, is to update the firmware.
the list of updates available on every laptop/desktop I receive is bonkers, and this is an enterprise laptop that have always been managed by corp IT, so you'd think they'd know.
on Linux it's super easy;
just type "sudo fwupdmgr update" and off you go.
You can also run "sudo fwupdmgr get-updates" to see what's there, give it a try!
#LinuxTips #Linux #Firmware
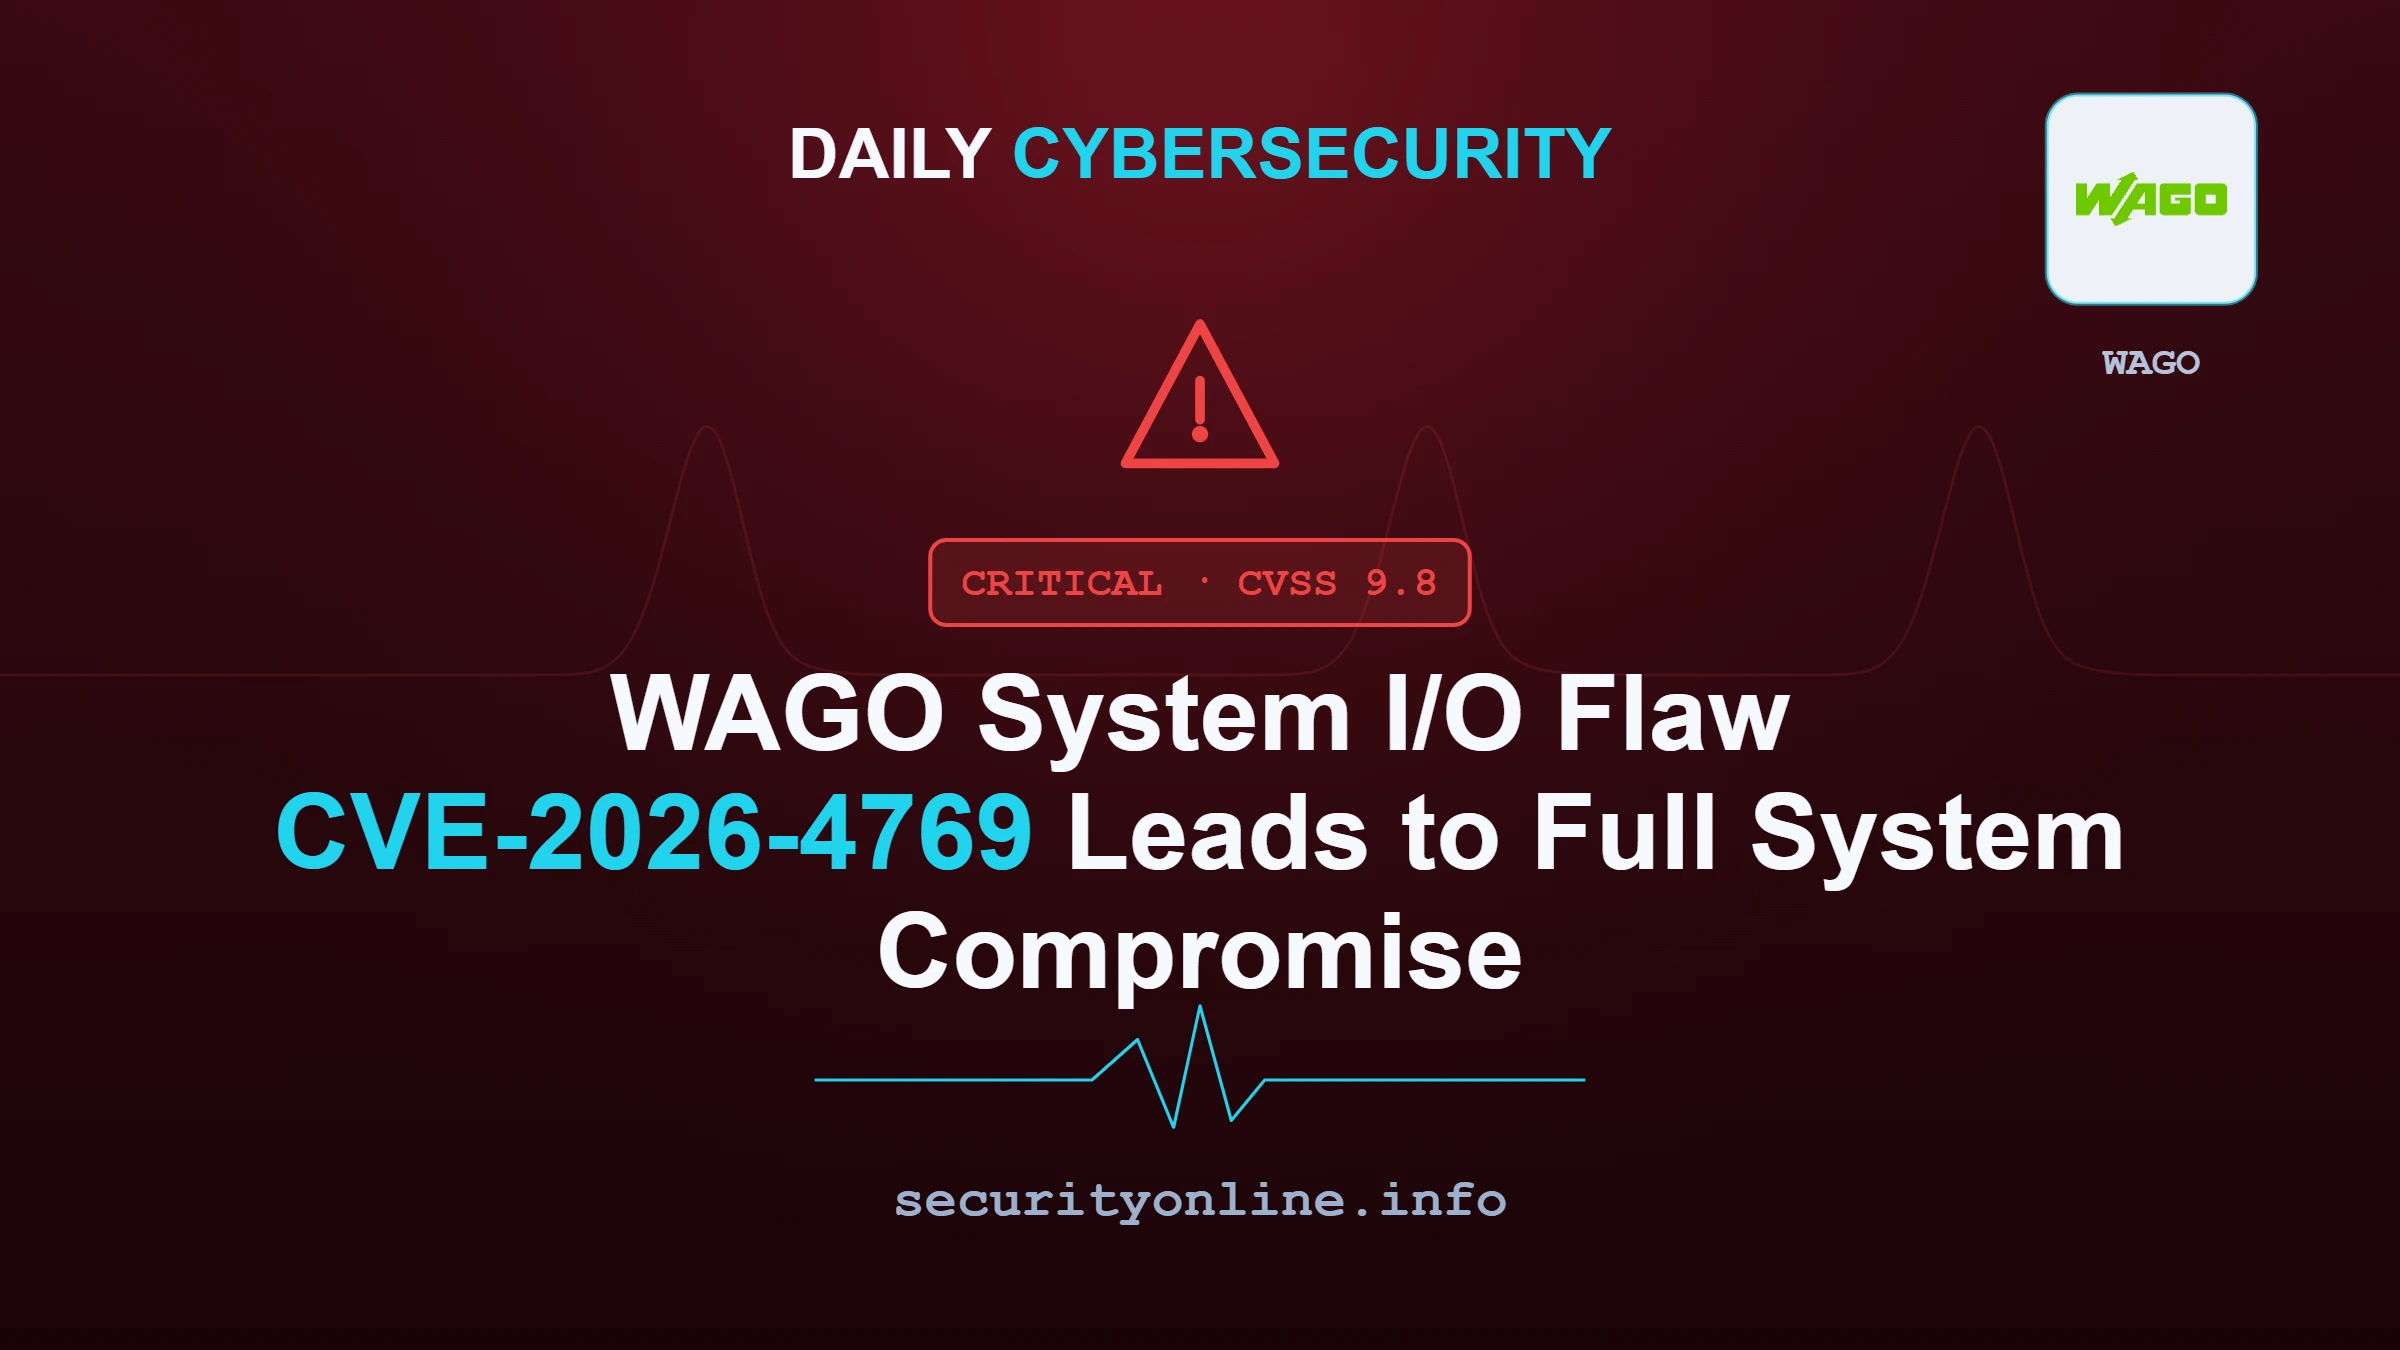
CVE-2026-4769 exposes WAGO System I/O field devices. An early-boot flaw lets an unauthenticated attacker reach full system compromise.
#WAGO #CVE20264769 #ICS #OTSecurity #Firmware
🤖 Six new U-Boot vulnerabilities discovered by Binarly. Two allow arbitrary code execution at boot — before OS security layers — enabling stealthy persistent firmware implants in routers, servers, and embedded devices.
🔗 https://www.bleepingcomputer.com/news/security/new-u-boot-flaws-could-enable-stealthy-firmware-attacks/
#Firmware #Exploit #Bootloader #CyberSec
Firmware update bricks Hue Bridge Pro devices; Philips gives free replacements
https://arstechnica.com/gadgets/2026/07/firmware-update-bricks-hue-bridge-pro-devices-philips-gives-free-replacements/
#SmartHome #Tech #Firmware
Undocumented Backdoor in Tenda Routers (CVE-2026-11405)
🔗 https://cybersecurefox.com/en/tenda-router-backdoor-cve-2026-11405
#tenda #router #backdoor #cve-2026-11405 #cert #cc #alert #firmware #vulnerability #rzadmin
Ich erwäge, den Server nachts abzuschalten und morgens zu starten. Leider gibt es bislang Probleme beim Reboot, wenn das System ein paar Tage gelaufen ist. Ganz zu schweigen davon, dass ich wohl #Podman Quadlets meistern und die automatisierte LUKS-Entschlüsselung sauber hinbekommen müsste. Aber eins nach dem anderen...
Also versuche ich, ob ein UEFI-Upgrade hilft. Also zuerst mal #BMC für #IPMI konfiguriert und darüber das Upgrade gemacht. So weit, so gut. ✅
Hab jetzt rausgefunden, dass man das Upgrade von #UEFI bei #SuperMicro wohl am Besten via Webinterface aktualisiert. Jetzt scheitere ich daran, dass ein Product Key verlangt wird. Erst mal schauen, wo ich den wieder her bekomme.
Und was habt Ihr heute so gemacht?
#Upgrade #Hardware #Firmware #Energiesparen #Stromsparen